UPCOMING WEBINAR:
The Shift Left and Secure Right Strategy for Financial Services in the Era of Frontier AI
- When: Tuesday, November 10, 1:00 pm ET - 1:30 pm ET
Enterprise MTTR averages 167 days. Mean time to exploit is minus 7 days. Exploits exist before patches do, then wait months for deployment.
Frontier AI models like Anthropic's Mythos are closing that gap from the wrong end, making vulnerability exploitation the top initial access vector for financial breaches. Every instinct says patch faster. But nothing gets 167 days faster, and financial institutions have the least room to try. So the strategy has to change shape rather than speed.
Today’s strategy requires shifting left and securing right simultaneously. Upstream, leveraging secure-by-default components minimizes the influx of vulnerabilities from the start; downstream, proactive mitigation serves as a core line of defense.
Join Steve Cobb and John Sapp Jr., Field CISOs at Zafran and Chainguard, on what that demands of financial services teams and where each shift runs out of road.
What We'll Cover:
-
Why time-to-exploit collapsed, and which assumptions frontier AI models invalidate
-
What replaces patch compliance as the exposure metric that holds up under DORA, NYDFS, and FCA scrutiny
-
What changes when you fix the starting point instead of working the backlog
-
How to use the controls already in your stack to neutralize reachable threats today
-
How Zafran's membership in Chainguard's Athena Coalition supports this strategy
Speaker
Speaker
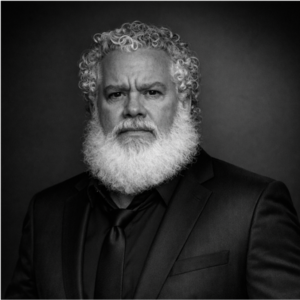
Steve Cobb
FIELD CISO, ZAFRAN
Steve Cobb, known across the industry as Cyber Santa, is Field CISO at Zafran, where he helps security leaders put Continuous Threat Exposure Management (CTEM) into practice and cut real exposure. With 30+ years in cybersecurity, incident response, and threat intelligence, he has led teams at Verizon, Microsoft, RBC, PNC Bank, and Capital One, and served as CISO of SecurityScorecard. Steve speaks often about the human side of security, from deepfakes to the rush to adopt AI, and leads with curiosity, communication, and service. A founding member of CarolinaCISO, he serves on several CISO boards, mentors the next generation of cyber talent, and speaks regularly at industry events.
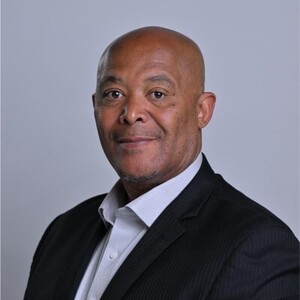
John Sapp Jr.
FIELD CISO, CHAINGUARD
John Sapp is Chainguard's Field CISO with over 35 years of experience across information technology, cybersecurity, and enterprise risk management. He is known for translating complex security challenges into clear business context and advising executives and Boards on risk-informed decisions. His expertise includes cybersecurity strategy, various domains of security with a specialization in application security, security operations, cyber risk governance, emerging technologies, and cyber resilience.